Which Messaging Apps Actually Encrypt by Default
Four popular messaging apps compared on default encryption, group chats, backups and metadata, because 'encrypted' means different things from app to app.
Signal, WhatsApp personal chats, and iMessage use end-to-end encryption by default. Ordinary Telegram cloud chats do not; its separate Secret Chats do. That answers the first question, but choosing a messenger also requires checking the copy saved for recovery and the information retained about your account.
This is a comparison of the providers’ published documentation, not a hands-on security audit. It covers personal text conversations and group chats, rather than every business integration, bot, channel, or AI feature inside these apps. A service’s encryption promise for one feature should not be assumed to cover another.
Defaults, groups, and recovery compared
End-to-end encryption (E2EE) protects message content so the service delivering it does not hold the keys needed to read it. Encryption between your device and a server protects that connection, but does not by itself exclude the server operator. Devices linked to an account and copies held by recipients still matter.
| App | Personal messages by default | Ordinary group messages | Backup or cloud-history protection | Information beyond message content |
|---|---|---|---|---|
| Signal | E2EE; see Signal’s privacy explanation | E2EE | Optional Secure Backups are E2EE; recovery key required | Sealed sender reduces sender information exposed during delivery; it is not an anonymity guarantee |
| E2EE for personal messages; see privacy guidance | E2EE for personal group chats | E2EE backups require enabling separately | Privacy policy describes usage, interaction, device, and connection information | |
| Telegram | Cloud chats use client-server encryption; E2EE requires a Secret Chat | Cloud groups are not E2EE | Cloud history is stored by Telegram; Secret Chats stay on their originating devices | Privacy policy describes cloud-message storage and collection of some metadata |
| iMessage | E2EE for iMessage, as distinct from other transports in the Messages app | E2EE when the conversation uses iMessage | Standard iCloud Backup is not E2EE; Advanced Data Protection changes this where available | Apple describes limited usage information, including iMessage eligibility checks; this does not establish a complete contact-history log |
Checked September 19, 2026 against the linked official documentation. Features and regional availability can change. Correction: an earlier version said Signal had only local backups and implied that any cloud backup exposes its key to the provider. Signal offers optional E2EE Secure Backups; cloud storage alone does not determine who can decrypt a backup.
Signal: recovery is a choice, not an impossibility
Signal’s current Secure Backups instructions describe an opt-in encrypted archive, protected by a 64-character recovery key that Signal does not receive. The free option includes text messages and recent media; the documentation specifies the last 45 days of media. A paid option extends media storage. The support page includes restoration instructions for Android and iOS.
That changes the practical decision. Losing a phone does not necessarily mean losing the history: an enabled backup and the recovery key can provide a recovery route. Without the key, Signal cannot decrypt that archive for you. Record it somewhere you can reach without the missing phone, and check that backups are actually enabled before relying on them.
Signal’s sealed-sender design addresses a different problem: the delivery envelope. It aims to hide the sender from the service while still allowing delivery to the destination. This reduces information exposure; it does not justify promising that no observer can infer who communicates with whom. Message content, delivery information, and device access are separate questions.
WhatsApp: check the backup setting separately
WhatsApp’s backup announcement distinguishes default encryption for personal conversations from the optional encrypted archive in Google Drive or iCloud. It documents password or encryption-key protection. Open the backup settings on your own phone and confirm the protection currently enabled; the existence of an encrypted live conversation is not evidence about its saved copy.
The privacy policy separately lists activity and interaction information, including time, frequency, and duration, as well as device and connection data. This supports a narrower statement than “Meta can always see everything about who you talk to.” Content encryption and service-data collection coexist, but a policy description is not a measurement of every record retained for every user.
For a hypothetical family group, the useful check is therefore shared: ask participants to review their backups too. Your own setting cannot control the copy on another participant’s phone. A group agreement about what belongs in chat can matter as much as choosing the app.
Telegram: a Secret Chat is a different conversation
Telegram’s FAQ separates cloud chats from device-specific Secret Chats. The latter use E2EE and do not synchronize through Telegram’s cloud. Ordinary group messaging remains outside that protection. Starting a Secret Chat is a deliberate step with an individual contact, not a switch that upgrades an existing group.
Its privacy policy says cloud messages are stored encrypted on its servers and describes automated analysis of cloud messages for spam and phishing. It also lists possible metadata collection, including IP addresses and devices. Saying those messages are not E2EE is accurate; saying they are stored as plaintext is not the same claim and is unnecessary.
Cloud synchronization may be useful for a community sharing public information. For a private group that requires content protection from the provider, however, a one-to-one exception does not meet the requirement. This is the same distinction between a default and a special feature that matters when comparing Fastmail and Proton.
iMessage: separate delivery from iCloud recovery
Apple’s Messages privacy page describes E2EE for iMessage. The Messages app also carries other message types, so the app’s name alone does not establish which transport a conversation uses. This comparison’s iMessage row should not be applied to every message displayed there.
Apple’s iCloud security table distinguishes standard protection from Advanced Data Protection. With standard protection, iCloud Backup keys are held by Apple. When both iCloud Backup and Messages in iCloud are enabled, the backup includes a copy of the Messages encryption key. With Advanced Data Protection, that backup and the key inside it are E2EE.
Availability is part of the decision: Apple’s UK notice says new UK users cannot enable Advanced Data Protection. Check the option available to your account rather than assuming everyone can turn it on. Where available, also understand the recovery method before changing protection. Disabling a backup without arranging another recovery route trades one risk for another.
A practical check before moving a group
Use the table to identify a requirement, then test the relevant workflow with non-sensitive example messages. The following is a proposed evaluation method, not a report of an experiment we conducted.
- Name the information to protect. Is the concern message content, group membership, a lost phone, or an administrator retaining access? Write down which matters most so a convenient feature does not silently replace the requirement.
- Identify the actual conversation type. Check an ordinary new group, not just a specially configured one-to-one chat. A reassuring app-wide slogan cannot answer whether that particular feature meets your need.
- Inspect recovery before migration. Note whether backup is enabled, who holds the recovery secret, and where it can be retrieved if the phone disappears. Do not erase your only copy to test recovery.
- Plan the exit. Decide which records belong outside chat, who is responsible for them, and whether an export is readable. Our guide to what an export contains helps distinguish a portable record from a file you cannot practically reuse.
- Agree on device and membership checks. Review linked devices and who should remain in the group. For a small team, the ownership questions in shadow software on teams remain relevant even when message encryption is strong.
E2EE does not prevent a recipient from copying a message or photographing the screen. Telegram’s own screenshot guidance makes that limitation explicit. A compromised or unlocked endpoint can also defeat the purpose of protecting delivery. Treat app selection as one part of handling sensitive information, not permission to send anything to anyone.
The strongest choice for a particular group is the one whose ordinary conversation mode, recovery arrangement, and membership practices meet that group’s stated needs. Default encryption is the starting point. The useful comparison follows the message through delivery, saved copies, and eventual recovery instead of awarding one permanent privacy score to an entire app.
Related reading
Encrypted Note Apps Compared: Who Can Read Your Notes, and What Each Plan Costs
Which note apps are end-to-end encrypted, what each paid plan costs, and how you get your notes back out — five apps checked against their own pages.
Cloud Backup Is Not Sync: What a Real Backup Costs and Who Holds the Keys
Six backup services compared on price, encryption, version history and restore — and why a synced folder is not a backup.
Who Holds the Keys to Your Email Inbox
Most email is encrypted in transit, but only some providers cannot read your inbox. Seven services compared on price, storage and who holds the keys.
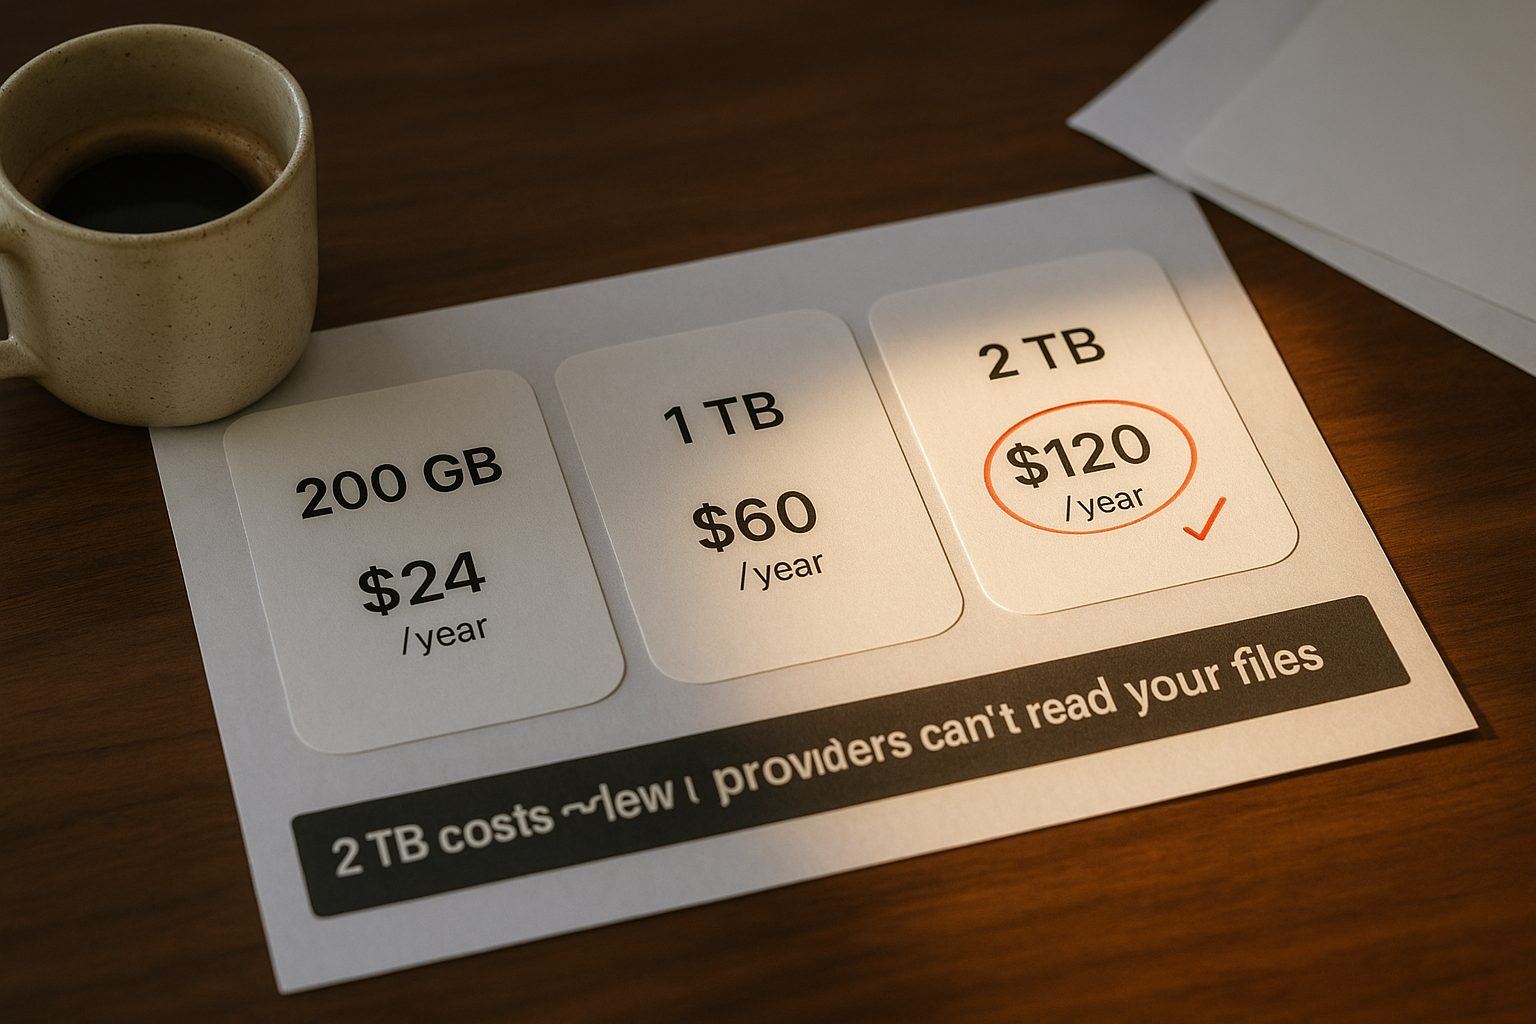
What Cloud Storage Actually Costs per Terabyte, and Who Can Read Your Files
Cloud storage pricing per terabyte: what nine providers charge a year, and which plans encrypt files so the provider cannot read them.